Employer Training & Business Skills
Cyber Security Awareness Training for Small Teams: What to Include
Build cyber awareness training around practical staff decisions, safe scenarios, clear incident reporting and relevant follow-up checks.
At a glance
Connect baseline awareness to your actual workplace procedures.
Practise verification and reporting with safe fictional scenarios.
Review understanding alongside technical protections.
Cyber security awareness training should help people make a safer decision during ordinary work: checking an unexpected request, using the approved sign-in method or reporting a suspected mistake quickly. A small team needs clear actions and an accessible reporting route, supported by appropriate technical controls. A completed quiz alone does not protect a business.
The National Cyber Security Centre’s free Top Tips for Staff package covers passwords, device security, phishing and incident reporting. It offers a useful starting point for staff with limited cyber knowledge. This guide explains how to connect that foundation to your own team, procedures and practice without turning every employee into a security specialist. (NCSC: Top Tips for Staff)
Start with the decisions your staff actually face
List a few realistic situations from your work: a supplier asks to change bank details, a colleague receives an unexpected sign-in prompt, a work phone is misplaced or an email attachment seems unusual. Use these to identify what the person should notice, what action they are authorised to take and whom they should contact.
Discuss the examples with the person responsible for IT or security before using them in training. The correct response must match your organisation’s systems. An employee should not have to invent a recovery procedure or decide independently whether a suspicious device is safe to reconnect. Keep the instruction short enough to use under pressure.
Include staff who work remotely, on shifts or without a desk. Check how they access guidance when their normal account or device is unavailable. Connect the learning with your induction programme, so new starters know the reporting route before they encounter a problem.
Build four practical learning outcomes
Use the NCSC package’s broad topics as a foundation, then write outcomes specific to your workplace. A password session should explain your approved account and authentication process. A device session should clarify who manages updates and what staff should do when a device is lost or behaves unexpectedly.
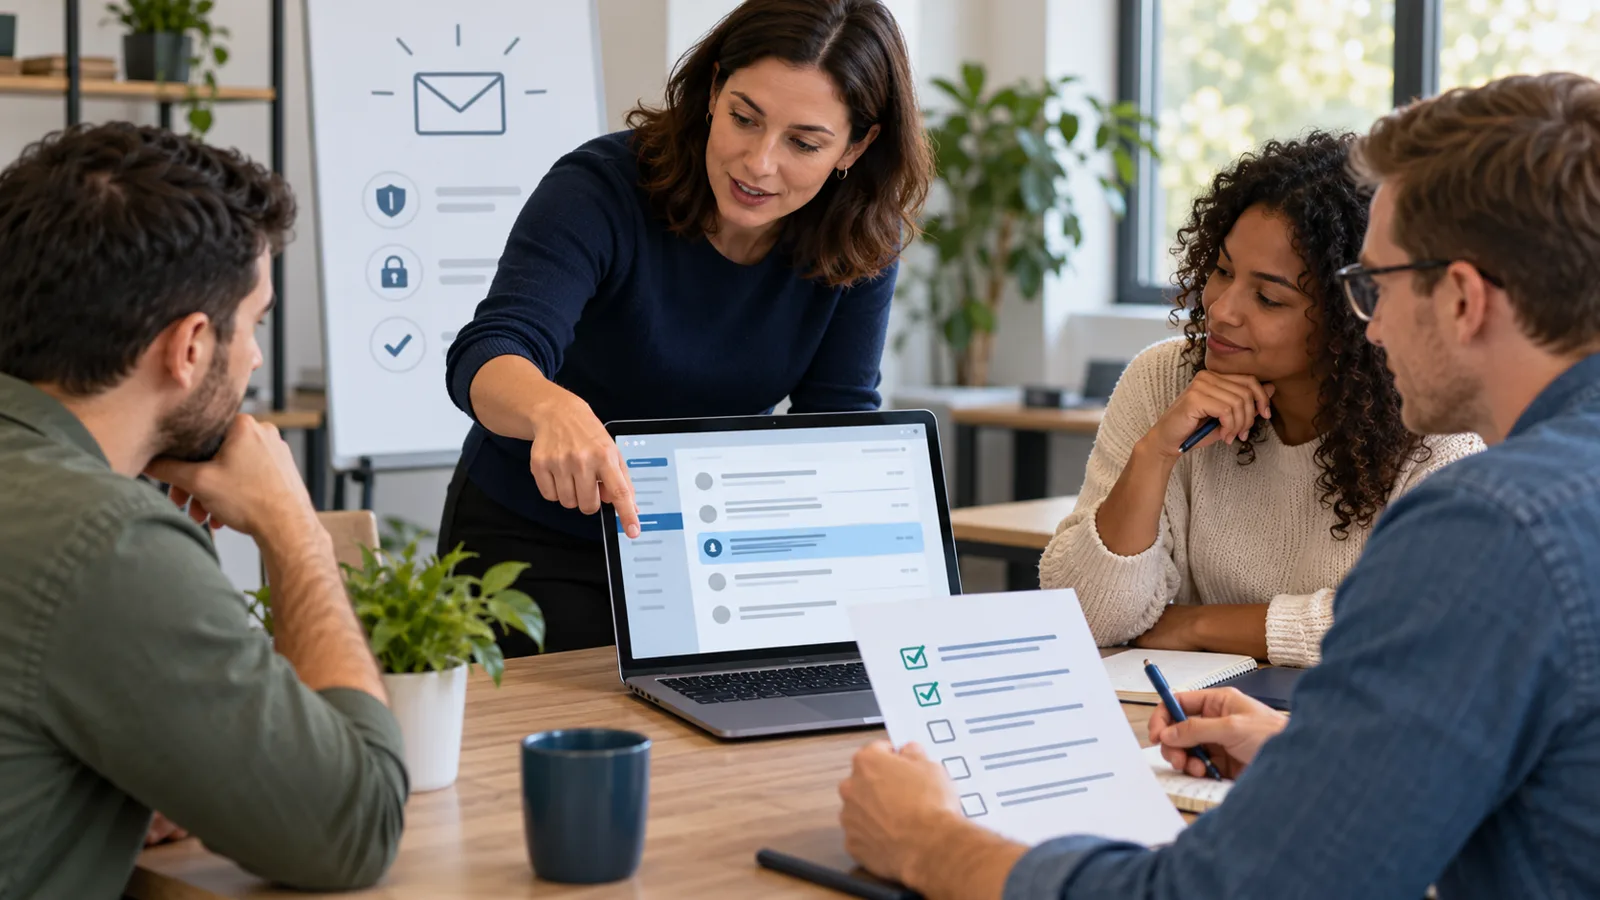
For suspicious messages, teach staff to pause and use an independently established route to verify an unusual request. A realistic-looking message or familiar display name is not enough. For reporting, show the exact contact or reporting control and explain what basic information is useful. Avoid asking staff to forward dangerous content casually around the team.
| Topic | Practice outcome | Organisation must provide |
|---|---|---|
| Accounts | Use the approved sign-in and recovery process | Clear instructions and authorised support |
| Devices | Recognise and report loss or unexpected behaviour | A usable reporting and response procedure |
| Suspicious requests | Verify through a known independent contact route | Agreed checks for sensitive changes |
| Incidents | Report promptly with relevant facts | A named route and backup contact method |
| Uncertainty | Ask before taking an unfamiliar risky action | Managers who support questions and escalation |
Practise with safe, fictional scenarios
Create a short fictional message asking for an urgent change to payment details. Ask the team what they would do next and which part of your procedure applies. The useful answer is a safe verification action, not simply a guess about whether the message is genuine. Do not use a real customer’s details or a functioning malicious link.
Run another exercise in which someone has already clicked an unexpected attachment. Ask what information they would report, how they would contact the responsible person and what instructions they would follow. This helps remove the mistaken idea that training only applies before an error. The response after a mistake matters too.
Keep exercises supportive. A public leaderboard of mistakes can discourage people from asking for help. If you consider simulated phishing, arrange it through an authorised, carefully scoped programme with appropriate review. You can teach the core decision-making through openly discussed examples without launching an unannounced test.
Make reporting easier than staying silent
Publish a clear contact route and a backup for when normal systems are unavailable. Explain what to report: what happened, when it happened, the affected account or device and any action already taken. Staff should not delay reporting while trying to prove that an incident has occurred.
Managers should respond calmly and avoid promising that a reported issue is harmless before it has been assessed. Separate the immediate need to contain and understand the situation from any later review. Tell the person what to do next and who owns the response. A short acknowledgement helps them know the report reached someone.
Check that your process works outside normal office hours where the business needs it. A poster naming one person is insufficient if nobody knows what happens during that person’s absence. Review contact details when roles or suppliers change, and make sure outsourced support responsibilities are understood.
Give training time and suitable access
Schedule learning during an appropriate work period and provide a usable device or alternative format. Ask about accessibility and language needs. An online module can introduce concepts, while a short team discussion connects them to your actual systems. Choose the delivery method through the same questions used when comparing classroom, online and workplace training.
Do not treat repeated difficulty as a reason to send someone the identical module indefinitely. Find the misunderstood step and offer a demonstration, simpler job aid or supported practice. Keep the learning focused on the task, then check whether the person can choose the right action in a different example.
A short awareness cycle
- Explain: introduce the risk in everyday language.
- Demonstrate: show the approved workplace action.
- Practise: use a fictional situation.
- Refresh: update guidance after changes and lessons learned.
Review behaviour and improve the system
Record completion, but also check whether staff can find the reporting route and explain how to verify a sensitive request. Review recurring questions and near misses for process improvements. More reports after training may reflect greater awareness rather than more attacks, so avoid interpreting one number without context.
Use realistic training evaluation to distinguish learning from wider security performance. Keep technical controls, access management and incident planning under the responsible owner’s review. Awareness training supports those measures; it does not certify that the organisation is secure or replace specialist assessment.
Common questions
Is a free training package enough for a small business?
It can provide a useful foundation, especially when it comes from an authoritative source such as the NCSC. You still need to connect it to your own systems, reporting contacts and working practices. Check that staff can apply the advice in their actual role, and maintain the technical protections that training cannot supply.
Should only IT staff receive cyber awareness training?
People outside IT also handle messages, documents, accounts and requests that can affect security. Give everyone relevant baseline guidance, then add role-specific learning where responsibilities differ. The person approving payments, for example, needs to understand the business’s verification process; they do not necessarily need a technical incident-response course.
How often should we repeat the training?
Choose a planned review cycle and add targeted refreshers when systems, procedures or risks change. A fixed calendar event should not delay correction of an unclear reporting route. Use questions and incident lessons to decide what needs reinforcement, rather than repeatedly presenting the same material without checking whether it remains useful.
What should an employee do after clicking a suspicious link?
They should promptly use the organisation’s reporting process and follow the responsible team’s instructions. They should describe what happened accurately rather than trying to hide it or improvise a technical investigation. The appropriate response depends on the circumstances, so training should make the reporting route and immediate approved procedure easy to find.
Can we use a real suspicious email in a training session?
Have the responsible security person prepare a safe example first. Remove personal or confidential information and ensure that attachments or links cannot cause harm. A fictional reconstruction often teaches the same decision more clearly. Avoid distributing the original message widely merely because the purpose is educational.
How should managers respond when someone reports a mistake?
Thank them for reporting, collect the essential facts and connect them with the agreed response process. Do not ask them to prove the issue is serious before escalating it. A calm, clear response helps the organisation learn what happened quickly, while any separate conduct or process review can follow the appropriate procedure.
Does passing a quiz prove someone will act safely?
A quiz can test recall, but it does not show every workplace behaviour. Add a short scenario in which the person explains the next action and finds the relevant contact or instruction. Use mistakes to identify a learning need, and check that the workplace procedure itself is clear and practical.
Should cyber training include AI tools?
Include relevant approved uses if staff encounter them, particularly information sharing and checking unexpected outputs. Keep the guidance tied to the organisation’s AI policy and permitted systems. A general cyber module may not address those details, so provide a separate briefing when the tool or its use introduces new decisions for staff.
Sources and further reading
- NCSC: Top Tips for Staff — free awareness training and its four core topics.
- GOV.UK: cyber security training for business — official training resources for staff and organisational leaders.